skip to main |
skip to sidebar
Sunday, July 21, 2013
Posted by
Corey Harrell
Mass injection attacks that compromise thousands of websites
are now a common occurrence on the Internet. One of the more recent attacks was
DarkLeech. Darkleech compromised thousands of servers running Apache which
resulted in iframes being injected into the websites to redirect their visitors
to malicious sites. Both the Sucuri Blog
and Unmask Parasites Blog do an
outstanding job talking about the artifacts left on the compromised servers.
The one perspective that doesn’t get discussed often is from the visitors’
computers who happen to browse to these compromised websites. This post
demonstrates how to perform a root cause analysis on an infected computer to
determine if the initial infection vector was the result of an injected iframe.
The Malware Indicator
Every malware incident starts with an indicator. In this
instance it was obvious the computer was infected with malware as can be seen
in the screenshots below.
A program named “S.M.A.R.T. Repair” started running on the
computer spitting up errors about the computer’s hard drive failing. The
malware went so far as trying to hide folders and files to make it appear even more
authenticate.
The Response
The purpose of this post is not to illustrate my examination
process. For that you can refer to my other posts such as Finding
Malware Like Iron Man, Malware
Root Cause Analysis, or Finding
the Initial Infection Vector. Instead my focus is on showing how the
artifacts I found on the system lead me to the injected hidden iframe.
Every story has a beginning so I have to at least fill in
the blanks about how I found the malware on this box. I initially grabbed the
volatile data with modified version of the tr3secure
volatile data collection script before taking the box offline. Looking at
the running processes I quickly flagged a few suspicious items.
These stood out since they are randomly named programs; a
great indicator by the way to identify malware. The process to executable
mapping revealed where these files were located.
Armed with the knowledge about two suspicious files (C:\ProgramData\WqPb9DQGxuSfxt.exe
and C:\ProgramData\VHuvoNRQPlUqRK.exe) I was able to quickly perform the root
cause analysis. This analysis is what lead me to the injected iframe on a
cached webpage.
My intention wasn’t even to discuss this examination; I
completed it over a year ago. I saw an email come across a listserv about
finding computers impacted by an injected iframe. After I read the email
exchanges I wondered how many people actually know how to determine if an
infected system was the result of an injected iframe or something else. I
wanted to shed light on the topic by illustrating how to do it.
**** Important *****
To protect the identity of all parties I have changed any
identifiable information. I altered user names, URLs, domain names, certain
values in URLs, dates, search terms, etc... Basically, everything you are
reading related to the infection has been altered except for the malicious
items. XMEN had nothing to do with the actual infection; I’m just a huge fan of
the XMEN. Also, for brevity I’m only showing some of the final timeline I put
together about the infection.
**** Important *****
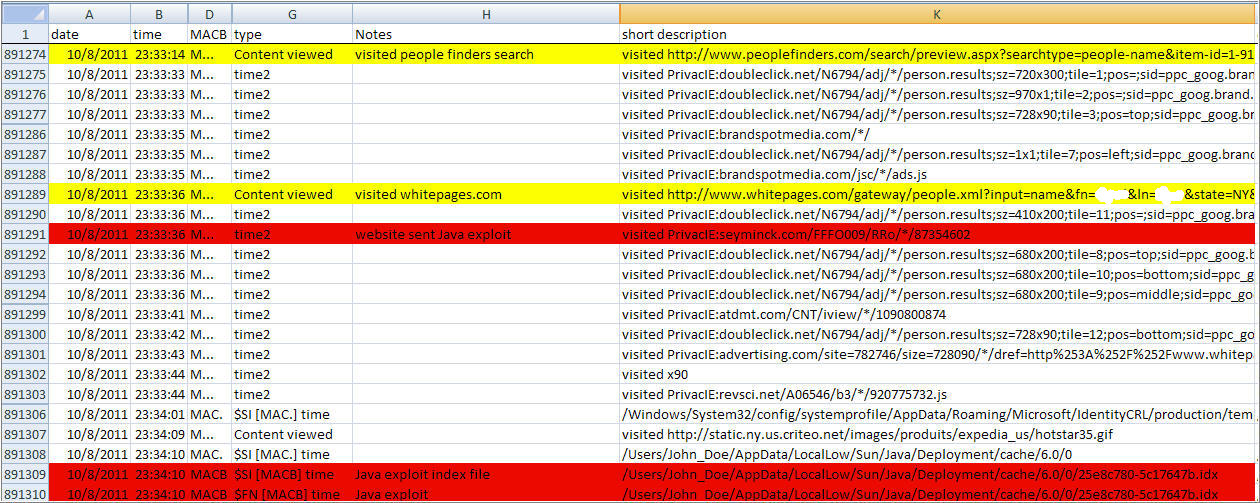
Following the Cookies Crumbs to an iframe
Searching for the malware I located in the volatile data
brought me to the point of interest in my timeline.
The Tracing
registry key showed a program named WqPb9DQGxuSfxt executed after the file
was created on the system. To find out what happened on the system I had to
look at the activity preceding the creation of the WqPb9DQGxuSfxt.exe file. The
picture below shows some of that activity.
The jusched.log file revealed that the Java application ran
around the time of this infection. Continuing on I found more interesting
artifacts.
The Shim
cache showed the presence of some other executables that were on the
computer around the time of interest. The browser history showed the system accessing
the URL hxxp://leynurivid.com. The web browsing activity continued on as shown
below.
Remember my disclaimer above? Fake data alert!! The user
visited a XMEN WordPress blog and the products page on the blog. Immediately
preceding this activity brought me closer to the initial infection vector as
shown in the picture below.
The 0.11512169499856473h7i.exe file’s name closely resembles
the pattern I’ve seen numerous times for downloaders dropped onto systems after
successful exploits. Not only was this the first reference to other file I
found in volatile data (C:\ProgramData\VHuvoNRQPlUqRK.exe) but there was another
artifact for Java execution. Can you guess what should appear next?
Immediately preceding the downloader and a modification to
the Java prefetch file were Java exploits. At the time I parsed these Java index
files manually since there were no tools available. However, at the time of
writing this post there are now a few tools including: Brian Baskin's Java Cache IDX Parser (I used this parser
for this post), Harlan’s
idx parser, or Mark Woan’s JavaIDX
parser. The 36158da7-67c256c0
file was a Java exploit and its index file (36158da7-67c256c0.idx)
contained the following:
IDX file:
36158da7-67c256c0.idx (IDX File Version 6.03)
[*] Section 2 (Download History) found:
URL: hxxp://marcelleoonard.aa.am/gipoto/yzjnbweofzjngtc9.jar
IP: 173.236.50.237
: HTTP/1.1 200 OK
content-length: 18799
last-modified: Tue, 17 Apr 2012 04:45:22 GMT
content-type: application/x-java-archive
date: Fri, 20 Apr 2012 12:39:55 GMT
server: Apache/2.2.3 (CentOS)
deploy-request-content-type: application/x-java-archive
The 10874ac5-7334b734
file was another Java exploit and its index file (10874ac5-7334b734.idx)
contained the following:
IDX file: 10874ac5-7334b734.idx (IDX File Version 6.03)
[*] Section 2 (Download History) found:
URL: hxxp://marcelleoonard.aa.am/gipoto/xuxvgpcwawdrdt.jar
IP: 173.236.50.237
: HTTP/1.1 200 OK
content-length: 9722
last-modified: Tue, 17 Apr 2012 04:45:22 GMT
content-type: application/x-java-archive
date: Fri, 20 Apr 2012 12:39:55 GMT
server: Apache/2.2.3 (CentOS)
deploy-request-content-type: application/x-java-archive
Both Java exploits were served up from the URL
hxxp://marcelleoonard.aa.am. Java wasn’t the only application that was targeted.
An Adobe Reader exploit was served up as well but the system
didn’t have this vulnerability. Notice the lack of Adobe Reader activity on the
system? In the midst of all this activity involving the marcelleoonard.aa.am
domain there was a cached webpage (xmen-steel_claws-for-sale[1].htm) from the
XMEN website.
The activity before the exploits appearing on the system
showed more Java execution artifacts and the XMEN webpage being accessed as
shown above. At this point in the analysis I identified the malware and then
traced the malware infection back to Java exploits. What was left was to
identify what served up the exploits which the preceding activity revealed as
shown below.
The activity that occurred before the exploits was web
browsing activity involving that hxxp://marcelleoonard.aa.am URL again. One
item was the cached webpage dabstepinattack[1].htm. Looking at the webpage code
was confirmation about its purpose.
The dabstepinattack[1].htm file served up the Java exploits
(xuxvgpcwawdrdt.jar and yzjnbweofzjngtc9.jar) and Adobe Reader exploit (grfoinbnktbq.pdf).
The last piece to the puzzle was to figure out what caused the dabstepinattack.php
page to appear. The preceding activity answered that question for me as shown
below.
All of the activity involving malware, Java exploits, Adobe
exploits, and the marcelleoonard.aa.am domain just stopped. There was only web
browsing activity of the user searching for wolverine steel claws which lead them
to the xmen-steel_claws-for-sale page on the XMEN website. Something on that
webpage resulted in the redirect to the exploits so I took a closer look at it.
In the cached xmen-steel_claws-for-sale webpage’s code showed there was an
injected iframe pointing to the dabstepinattack.php page on
marcelleoonard.aa.am domain.
In Closing
Systems will visit the thousands of websites compromised in
mass injection attacks. If these systems have client-side vulnerabilities then
mostly likely some of them will cross our paths due to them getting infected.
To tie the initial infection vector back to a mass injection campaign all you
need to do is locate the injected iframe at the top or bottom of the cached
webpage.
Sunday, July 29, 2012
Posted by
Corey Harrell
Wednesday, April 25, 2012
Posted by
Corey Harrell
Volume Shadow Copies has been my main focus on the blog for the past few months. I took the time needed to share my research because I wanted to be thorough so others could use the information. As a result, the interesting linkz I’ve been coming across have piled up in my hopper. In this Linkz post I’m cleaning out the hopper. There are linkz about: free DFIR e-magazines, volume shadow copies, triage, timeline analysis, malware analysis, malware examinations, Java exploits, and an interesting piece on what you would do without your tools. Phew …. Let’s roll
Into The Boxes has Returned
Into The Boxes is an e-magazine discussing topics related to Digital Forensic and Incident Response. When the magazine was first released a few years ago I saw instant value in something like this for the community. A resource that not only provides excellent technical articles about DFIR but also compliments what is already out there in the community. I really enjoyed the first two editions but a third issue was never released…. That is until now. The ITB project is back up and running as outlined in the post Into The Boxes: Call for Collaboration 0×02 – Second Try.
It looks like ITB won’t be the only free DFIR magazine on the block. Lee Whitfield is starting up another free magazine project called Forensic 4cast Magazine. His magazine will also be discussing topics related to Digital Forensic and Incident Response.
It’s great to see projects like these but they will only be successfully with community support such as feedback and more importantly writing articles. Without support then efforts like these will go to where great ideas go to die. I’m willing to step up to the plate to be a regularly contributor of original content. I’ll be writing for ITB and my first article discusses how to find out how a system was infected after I.T. tried to clean the infection. Cleaning a system makes it harder to answer the question of how but it doesn’t make it impossible. Stay tuned to see what artifacts are left on a cleaned system in an upcoming ITB edition.
RegRipper Plugins Maintenance Perl Script
This link is cool for a few reasons. Sometime ago Cheeky4n6Monkey sent me an email introducing himself and asking if I had any project ideas. I knew who Cheeky was even before his introductory email because I’ve been following his outstanding blog. I thought this was really cool; he is looking to improve his DFIR skills by trying to reach out and help others. He isn’t taking a passive approach waiting for someone to contact him but he is doing the complete opposite. I went over my idea hopper and there was one thing that has been on my to-do list for some time. At times I wanted to review the RegRipper profiles to update the plugins listed. However, I didn’t want to manually review every plugin to determine what the profile was missing. A better approach would be to flag each plugin not listed which would then reduce the number of plugins I had to be manually review. I mentioned the idea to Cheeky and he ran with it. Actually he went warp speed with the idea because he completed the script within just a few days. To learn more about his script and how to use it check out the post Creating a RegRipper Plugins Maintenance Perl Script.
VSC Toolset
The one thing I like about the DFIR community is the people who willingly share information. Sharing information not only educates us all thus making us better at our jobs but it provides opportunities for others to build onto their work. Case in point, I didn’t start from scratch with my Ripping VSCs research since I looked at and built on the work done by Troy Larson, Richard Drinkwater, QCCIS, and Harlan. I was hoping others would take the little research I did and take it another step forward. That is exactly what Jason Hale from Digital Forensics Stream did. Jason put together the VSC Toolset: A GUI Tool for Shadow Copies and even added additional functionality as outlined in the post VSC Toolset Update. The VSC Toolset makes it extremely easy for anyone to rip VSCs and to add additional functionality to the tool. Seriously, it only takes one line in a batch file to extend the tool. Jason lowered the bar for anyone wanting to examine VSCs using this technique.
Triage Script
When I put together the Tr3Secure Data Collection script I was killing two birds with one stone. First and foremost, the script had to work when responding to security incidents. Secondly, the script had to work for training purposes. I built the script using two different books so people could reference them if they had any questions about the tools or the tools’ output. As such, the one limitation with the Tr3Secure Data Collection is it doesn’t work remotely against systems. Michael Ahrendt (from Student of Security) released his Automated Triage Utility and has since updated his program. One capability Automated Triage Utility has is being able to run against remote systems. To see how one organization benefited by Michael’s work check out Ken Johnson (from Random Thoughts of Forensic) post Tools in the Toolbox – Triage. If you are looking for triage scripts to collect data remotely then I wouldn’t overlook Kludge 3.0. The feedback about Kludge in the Win4n6 Yahoo group has been very positive.
HMFT – Yet Another $MFT extractor
Speaking about Triage, Adam over at Hexacon recently released his HMFT tool in the post HMFT – Yet Another $MFT extractor. I was testing out the script and it grabbed an MFT off a live Windows 7 32 bit Ultimate system within a few seconds. One area where I think HMFT will be helpful is in triage scripts. Having the ability to grab a MFT could provide useful filesystem information including the ability to see activity on a system around a specific time of interest. I plan on updating the Tr3secure Data Collection script to incorporate HMFT.
Strings for Malware Analysis
While I’m talking about Adam I then I might as well mention another tool he released. Sometime ago he released the HAPI – API extractor. The tool will identify all the Windows APIs present in a file’s strings. I’ve been working my way through Practical Malware Analysis (except a full review soon) and one of the steps during static analysis is reviewing a file’s strings. Identifying the Windows APIs in strings may give a quick indication about the malware’s functionality and HAPI makes it so much easier to find the APIs. I added the tool to my toolbox and it will be one of the tools I run whenever I’m static analysis against malware.
Need for Analysis on Infected Systems
Harlan recently discussed the need to perform analysis on infected systems as a means to gather actionable intelligence. His first post where this was mentioned was The Need for Analysis in Intelligence-Driven Defense while the second one was Updates and Links. Alright, Harlan made a lot of great points in those both besides the need to analysis infected systems and they are both definitely worth the read. I’ve heard discussions among digital forensic practitioners about performing analysis on infected systems to determine how the infection occurred. A few responses included: it’s too hard, too time consuming, or most of the time you can’t tell how the infection occurred. People see the value in the information learned by performing an examination but there is no follow through by actually doing the exam. It makes me wonder if one of the roadblocks is that people aren’t really sure what they should be looking for since they don’t know what the Attack Vector Artifacts look like.
NTFS INDX Files
Sometime time ago William Ballenthin released his INDXParse script that can be used to examine NTFS INDX files. To get a clearer picture about the forensic significance of INDX files you can check out Chad Tilbury’s post NTFS $I30 Index Attributes: Evidence of Deleted and Overwritten Files in addition to the information provided by William Ballenthin. INDXParse comes with an option to use a bodyfile as the output (-b switch) and this can be used to add the parsed information to a timeline. Don’t forget that next week William Ballenthin is presenting about his INDX files research in a DFIROnline special edition.
Colorized Timeline Template
Rob Lee created a timeline template to automate colorizing a timeline when imported into Excel. His explanation about the template can be found on his post Digital Forensic SIFTing: Colorized Super Timeline Template for Log2timeline Output Files. Template aside, the one thing I like about the information Rob shared is the color coding scheme to group similar artifacts. To name a few: red for program execution, orange for browser usage or yellow for physical location. Using color in a timelines is a great idea and makes it’s easier to see what was occurring on a system with a quick glance.
Checklist to See If A System's Time Was Altered
Rounding out the posts about time is Lee Whitfield’s slide deck Rock Around the Clock. In the presentation, Lee talks about numerous artifacts to check to help determine if the time on the system was altered. After reading his slides over and the information he provided makes a great checklist one could follow if a system’s time comes into question. The next time I need to verify if someone changed the system clock then I’ll follow these steps as outlined by Lee. I copied and pasted my personal checklist so if any information is listed below that didn’t come from Lee’s slide deck then I picked it up from somewhere else.
- NTFS MFT entry number
* New files are usually created in sequence. Order files by creation then by identifier. Small discrepancies are normal but large require further investigation
- Technology Advancement
* Office, PDF, Exif images, and other items' metadata show program used to create it. Did the program exist at that time?
- Windows Event Logs
* Order event logs in order then review the date/time stamps that are out of order
* XP Event ID 520 in security log "the system time was changed" (off by default) Vista, 7 Event ID 1 in system log "the system time has changed to ..." and event id 4616 in security log "the system time was changed"
- NTFS Journal
* Located in the $J stream of $UsnJrnl and may hold few hours or days of data. Entries sequentially stored
- Link files
* XP each link file has a sequence number (fileobjectid). Sort by creation date then review sequence number
- Restore Points
* XP restore points named sequentially. Sort by creation date then review RP names for out of sequence
- Volume Shadow Copies
* VSC GUIDs are similarly named for specific times
* Sort by creation data and then review the VSC names to identify ones out of place
- Web pages (forums, blogs, or news/sports sites)
* Cached web pages may have date/time
- Email header
- Thumbnails
* XP one repository for each folder and Vista/7 one for all folders. Both store items sequentially.
* Sort by file offsets order then review for out of place dates
Attackers Are Beating Java Like a Red Headed Stepchild
I don’t have much narration about Java exploits since I plan on blogging about a few case experiences involving it. I had these links under my exploits category and wanted to get rid of them so I can start fresh. Towards the end of last year a new Java vulnerability was being targeted and numerous attacks started going after it. DarkReading touched on this in the article The Dark Side Of Java and Brian Krebs did as well in the post New Java Attack Rolled Into Exploit Kits. The one interesting thing about the new Java attack from the DFIR perspective is it looks the same on a system as other Java exploits going after different vulnerabilities. It’s still good to be informed about what methods the attackers are using. Another link about Java was over at the Zscaler Threatlab blog. There’s an excellent write-up showing how a Java Drive-by Attack looks from the packet capture perspective.
What Can You Do Without Your Tools
The Security Shoggoth blog's post Tools and News provided some food for thought. The post goes into more depth on the author’s tweet: Want to find out how good someone is? Take away all their tools and say, "Now do it.". When I first got started in DFIR I wanted to know the commercial tool I had available inside and out. I learned as much as I could about the tool except learning how to write enscripts. Then one day I thought to myself, could I do forensics for another shop if they don’t have Encase and the answer was unfortunately no. I think there are a lot of people in our field who fall into the on commercial tool boat. They can do wonders with their one tool but if they don’t have access to it or if the tool can’t do something then they get stuck. I made the decision to improve my knowledge and skills so I could do my job regardless of the tools I had available. The change didn’t happen overnight and it took dedication to learn how to do my job using various tools for each activity. Try to answer two of the questions the author mentioned in his post and if you are unable to fully answer them then at least you know an area needing improvement.
Imagine for a moment that you didn't have the tool(s) you use most in your job - how would you perform your job? What alternatives are available to you and how familiar you are with them?
Monday, March 19, 2012
Posted by
Corey Harrell
The one thing I like about sharing is when someone opens your eyes about additional information in an artifact you frequently encounter. Harlan has been posting about prefetch files and the information he shared changed how I look at this artifact. Harlan’s first post Prefetch Analysis, Revisited discussed how the artifact contains strings -such as file names and full paths to modules that were either used or accessed by the executable. He also discussed how the data can not only provide information about what occurred on the system but it could be used in data reduction techniques. One data reduction referenced was searching on the file paths for words such as temp. Harlan’s second post was Prefetch Analysis, Revisited...Again... and he expanded on what information is inside prefetch files. He broke down what was inside a prefetch from one of my test systems where I ran Metasploit against a Java vulnerability. His analysis provided more context to what I found on the system and validated some of my findings by showing Java did in fact access the logs I identified. Needless to say, his two posts opened my files to additional information inside prefetch files. Additional information I didn’t see the first the first time through but now I’m taking a second look to see what I find and to test out how one of Harlan's data reduction techniques would have made things easier for me.
Validating Findings
I did a lot of posts about Java exploit artifacts but Harlan did an outstanding job breaking down what was inside one of those Java prefetch files. I still have images from other exploit artifact testing so I took a look at prefetch files from an Adobe exploit and Windows Help Center exploit. The Internet Explorer prefetch files in both images didn’t contain any references to the attack artifacts but the exploited applications’ prefetch files did.
The CVE-2010-2883 (PDF Cooltype) vulnerability is present in the cooltype.dll affecting certain Adobe Reader and Acrobat versions. My previous analysis identified the following: the system had a vulnerable Adobe reader version, a PDF exploit appeared on the system, the PDF exploit is accessed, and Adobe Reader executed. The strings in the ACRORD32.EXE-3A1F13AE.pf prefetch file helped to validate the attack because it shows that Adobe Reader did in fact access the cooltype.dll as shown below.
\DEVICE\HARDDISKVOLUME1\PROGRAM FILES\ADOBE\READER 9.0\READER\COOLTYPE.DLL
The prefetch file from the Windows Help Center URL Validation vulnerability system showed something similar to the cooltype.dll exploit. The Seclists Full disclosure author mentioned that Windows Media Player could be used in an attack against the Help Center vulnerability. The strings in the HELPCTR.EXE-3862B6F5.pf prefetch file showed the application did access a Windows Media Player folder during the exploit.
\DEVICE\HARDDISKVOLUME1\DOCUMENTS AND SETTINGS\ADMINISTRATOR\LOCAL SETTINGS\APPLICATION DATA\MICROSOFT\MEDIA PLAYER\
Finding Malware Faster
Prefetch files provided more information about the exploit artifacts left on a system. By itself this is valuable enough but another point Harlan mentioned was using the strings inside prefetch files for data reduction. One data reduction technique is to filter on files' paths. To demonstrate the technique and how effective it is at locating malware I ran strings across the prefetch folder in the image from the post Examining IRS Notification Letter SPAM. (note, strings is not the best tool to analyze prefetch files and I’m only using the tool to illustrate how data is reduced) I first ran the following command which resulted in 7,905 lines.
strings.exe –o irs-spam-email\prefetch\*.pf
I wanted to reduce the data by only showing the lines containing the word temp to see if anything launched from a temp folder. To accomplish this I ran grep against the strings output which reduced my data to 84 lines (the grep -w switch matches on whole word and –i ignores case).
strings.exe –o irs-spam-email\prefetch\*.pf | grep –w –i temp
The number of lines went from 7,905 down to 84 which made it fairly easy for me to spot the following interesting lines.
\DEVICE\HARDDISKVOLUME1\DOCUME~1\ADMINI~1\LOCALS~1\TEMP\TEMPORARY DIRECTORY 1 FOR IRS%20DOCUMENT[1].ZIP\IRS DOCUMENT.EXE
\DEVICE\HARDDISKVOLUME1\DOCUME~1\ADMINI~1\LOCALS~1\TEMP\PUSK3.EXE
Using one filtering technique enabled me to quickly spot interesting executables in addition to the possibly finding the initial infection vector (a malicious zip file). This information was obtained by running only one command against the files inside a prefetch folder. In hindsight, my original analysis on the prefetch files was fairly limited (executable paths, runcounts, and filenames) but going forward I'll look at this artifact and the information they contain in a different light.
Sunday, November 20, 2011
Posted by
Corey Harrell
There are different ways to spread malware. Email, instant messaging, removable media, or websites are just a few options leveraged to infect systems. One challenge when performing an examination is determining how the malware ended up on the system which is also referred to as identifying the malware’s initial infection vector (IIV). A few obstacles in determining the IIV is that a system changes over time: files are deleted, programs are installed, temporary folders are emptied, browser history is cleared, or an antivirus program cleaned the system. Every one of those obstacles may hinder the examination. However, they don’t necessary result in not being able to narrow down the IIV since some artifacts may still be present on the system pointing to the how.
There are various reasons provided why an examination isn’t performed on a malware infected system to locate the IIV. I first wanted to point out why taking the time to find the IIV is beneficial instead of focusing on the reasons why people don’t. The purpose of the root cause analysis is to identify the factors lead up to the infection and what actions need to be changed to prevent the reoccurrence of a similar incident. If the infected system is just cleaned and put back into production then how can security controls be adjusted or implemented to reduce malware infecting systems in a similar manner? Let’s see how this works by skipping the root cause analysis and placing blame on a user opening a SPAM email. A new security awareness initiative educates employees on not opening SPAM email which does very little if the malware was a result of a break down in the patch management process. Skipping figuring out the IIV is not only a lost opportunity for security improvements but it prevents knowing when the infection first occurred and what data may have been exposed. This applies to both organizations and individuals.
Determining how the malware infected a system is a challenge but that's not a good enough reason to not try. It may be easier to say it can’t be done, takes too much resources or it's not worth it since someone (aka users) never listen and did something they weren’t suppose to. As a learning opportunity I’m sharing how I identified the initial infection vector in a recent examination by showing my thought process and tool usage.
First things first… I maintain the utmost confidentiality in any work I perform whether if it’s DFIR or vulnerability assessments. At times on my blog I write detailed posts about actual examinations I performed and every time I’ve requested permission to do so. This post is no different. I was told I can share the information for the greater good since it may help educate others in the DFIR community who are facing malware infected systems.
Background Information
People don’t treat me as their resident “IT guy” to fix their computer issues anymore. They now usually contact me for another reason because they are aware that I’ve been cleaning infected computers for the past year free of charge. So it’s not a strange occurrence when someone contacts me saying their friend/colleague/family member/etc appears to be infected with a virus and needs a little help. That’s pretty much how this examination came about and I wasn’t provided with any other information except for two requests:
* Tell them how the infection occurred so they can avoid this from happening again
* Remove the viruses from the computer
Investigation Plan
The methodology used throughout the examination is documented on the jIIr Methodology Page. I separated the various system examination steps into the first three areas listed below.
1. Verify the system is infected
2. Locate all malware present on the system
3. Identify the IIV
4. Eradicate the malware and reset any system changes
I organized the areas so each one will build on the previous one. My initial activities were to verify that the system was actually infected as opposed to the requester interpreting a computer issue as an infection. To accomplish this I needed to locate a piece of malware on the system either through antivirus scanning or reviewing the system auto-run locations. If malware was present then the next thing I had to do was locate and document every piece of malware on the computer by: obtaining general information about the system, identifying files created around the time frame malware appeared, and reviewing the programs that executed on the system. The examination would require since the technique excels at highlighting malware on a system. The third area and the focus of this post was to identify the initial infection vector. The IIV is detected by looking at the system activity in the timeline around the timeframe when each piece of malware was dropped onto the system. The activity can reveal if all of the malware is from the same attack or if there were numerous attacks resulting in different malware getting dropped onto the system. The final area is to eradicate every malware identified.
Note: Some activities were conducted in parallel to save time. To make it easier for people to follow my examination I identified each activity with the symbol <Step #>, the commands I ran are in bold, and registry and file paths are italicized.
Verifying the Infection
The computer’s hard drive was connected to my workstation and a software write blocker prevented the drive from being modified. I first reviewed the master boot record (MBR) to see the drive configuration I was dealing with and to check for signs of MBR malware <Step 1>. I ran the Sleuthkit command: mmls.exe -B \\.\PHYSICALDRIVE1 (the -B switch shows the size in bytes). There was nothing odd about the hard drive configuration and I found out that additional time was needed to complete the examination since I was dealing with a 500 GB hard drive. To assist with identifying known malware on the system I fired off a Kaspersky antivirus scan against the drive <Step 2>.
Knowing the antivirus scan was going to take forever to complete I moved on to checking out the system’s auto-runs locations for any signs of infection. The Sysinternals AutoRuns for Windows utility was executed against the Windows folder and the only user profile on the system <Step 3>. In the auto-runs I was looking for unusual paths launching executables, misspelled file names, and unusual folders/files. It wasn’t long before I came across an executable with a random name in the HKCU\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon\Shell registry key.
The HKCU\Software\Microsoft\Windows\CurrentVersion\Run registry key also listed under Auto-runs Logon tab showed that the C:\Users\John_Doe\AppData\Roaming folder had more than just one randomly named executable. The key also showed an additional location which was the C:\Users\John_Doe\AppData\Roaming\Microsoft folder.




 Posts

